Cyber Attacks
Should I Use Password Managers: Security Risks and Best Practices
Password managers reduce credential reuse but create a single high-value target that requires strict master password hygiene and offline backup strategies.
Password managers reduce credential reuse but create a single high-value target that requires strict master password hygiene and offline backup strategies.
Virtual private clouds share physical hardware with other tenants, whereas private clouds dedicate infrastructure to a single organisation, creating distinct risk profiles.
Full disk encryption secures data at rest but leaves it exposed while running in memory, creating a distinct gap in your defence strategy.
Runtime controls catch compromised containers that build-time scans miss, but they consume host resources and require careful tuning to avoid breaking services.
Personal data loses its protected status when combined with innocuous fragments, turning routine logs into high-value targets for identity fraud.
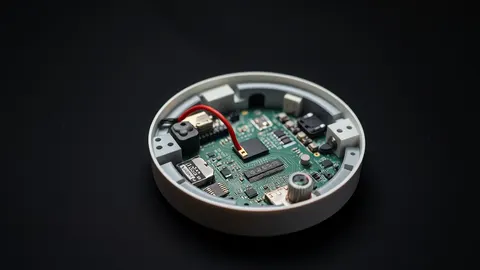
Firmware updates often introduce new attack surfaces and require strict cryptographic verification to prevent persistent compromise of hardware devices.
Privileged access management breaks the link between identity and persistent power, ensuring that elevated rights exist only for the duration of a specific task.
Volatile memory holds encryption keys and process trees that disappear when the power cuts, offering a view of active threats that disk scans cannot see.
Blue team operations transform raw noise into actionable context, shifting defence from passive logging to active hypothesis testing and adversary modelling.
Most injection attacks bypass perimeter controls by hiding inside legitimate processes, making internal integrity checks the only reliable defence.
Private endpoints keep traffic on the internal network backbone, preventing it from touching the public internet even when accessing public cloud services.
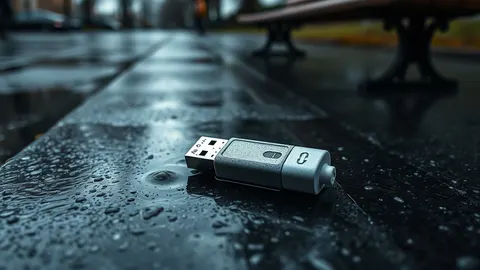
Baiting attacks rarely rely on flashy malware; they succeed by exploiting human curiosity and the lack of visibility into peripheral storage devices.
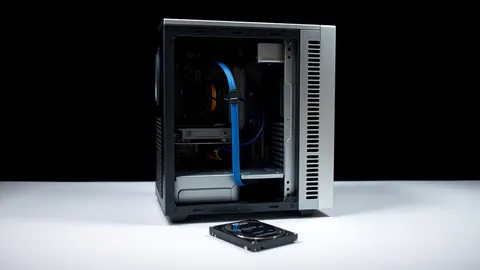
Wiping a drive rarely removes firmware implants or memory-resident agents, making pre-imaging forensics mandatory for true recovery.
Traditional signature matching misses novel attacks, requiring behavioural analysis and endpoint isolation to stop ransomware before encryption begins.
YARA rules detect malware families by structural patterns rather than hashes, allowing them to identify new variants that traditional signature systems overlook entirely.
Most small firms lose data not through external hacks, but because they never mapped where sensitive information actually resides on their network.
Default credentials often hide in plain sight, masquerading as valid accounts within complex network traffic rather than obvious login failures.
Fake login windows mimic real browser frames to steal credentials from users who trust their own eyes and ignore address bar warnings.
DKIM signatures validate message integrity, not sender identity, meaning a valid signature only proves the content has not changed since the domain owner signed it.
Attackers rarely leak your data; they prioritise quiet payment over public shame because exposure invites law enforcement scrutiny and reduces their long-term profitability.
Unified visibility fails when public clouds hide metadata, leaving hybrid environments blind to lateral movement between distinct networks.
Paying ransomware operators often accelerates future attacks, while refusing payment shifts the burden to internal recovery capabilities and forensic investigation.
Temporary controls shift risk rather than removing it, creating hidden complexity that often outlives the original vulnerability.
Dark web monitoring relies on crawling hidden forums and marketplaces, but it often misses real-time leaks and struggles with encrypted communication channels that bypass traditional indexing.