Data Breaches
Data Retention Policy Mistakes and How to Avoid Them
Retaining data beyond its operational life creates an attack surface that grows with every day you delay deletion, turning old logs into permanent liabilities.
Data Breaches coverage from Honeypot Daily holds 19 articles, 15 of them reference guides. The newest was published on October 14, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include NIST Cybersecurity Framework and UK Information Commissioner's Office.
Retaining data beyond its operational life creates an attack surface that grows with every day you delay deletion, turning old logs into permanent liabilities.

Forensic analysis fails when the initial imaging process alters the original data, rendering legal evidence inadmissible regardless of the findings.
Public profile details combine with passive data collection to bypass multi-factor authentication and verify identities for credential theft without direct interaction.
Salting prevents attackers from using precomputed rainbow tables to reverse your entire database in a single pass.
Keeping data longer than necessary increases attack surface and legal exposure while raising infrastructure costs without adding business value.
Tokenization fragments text into mathematical units that obscure original meaning, creating hidden vectors for data leakage and inference attacks.
Static card numbers are useless to attackers once you replace them with single-use tokens that expire after one transaction.
A digital forensics analyst reconstructs events from binary residues, proving that silence in logs is often louder than noise.
The Norwegian Data Protection Authority has penalised Xandr for processing sensitive Grindr user data without a valid legal basis.
A trivial administrator password at a Danish IT firm allowed an attacker to access millions of national ID records via a legitimate portal.
Dutch and Israeli researchers identified 8,547 exposed wind and solar control systems across thirty-five countries, raising urgent operational security concerns for energy operators.
Full disk encryption secures data at rest but leaves it exposed while running in memory, creating a distinct gap in your defence strategy.
Personal data loses its protected status when combined with innocuous fragments, turning routine logs into high-value targets for identity fraud.
A former engineer deleted admin accounts and reset passwords, demanding cryptocurrency to prevent further damage to the company’s critical infrastructure servers.
Most small firms lose data not through external hacks, but because they never mapped where sensitive information actually resides on their network.
Attackers rarely leak your data; they prioritise quiet payment over public shame because exposure invites law enforcement scrutiny and reduces their long-term profitability.
Dark web monitoring relies on crawling hidden forums and marketplaces, but it often misses real-time leaks and struggles with encrypted communication channels that bypass traditional indexing.
Attackers wait for a child to reach adulthood before cashing in stolen data, allowing fraud to compound silently for over a decade without detection.
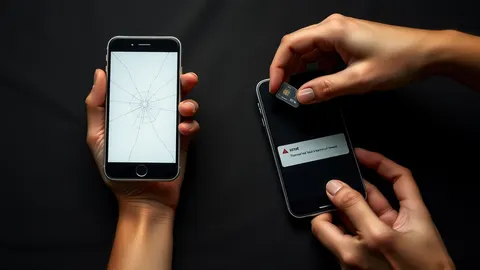
Attackers bypass your phone's security by convincing the carrier to move your number to a new device, rendering two-factor authentication useless.