Threat Intelligence
Windows Event Log Monitoring: Signal, Noise and Strategic Limits
Most teams drown in noise because they treat every log entry as intelligence rather than filtering for specific behavioural anomalies.
Most teams drown in noise because they treat every log entry as intelligence rather than filtering for specific behavioural anomalies.
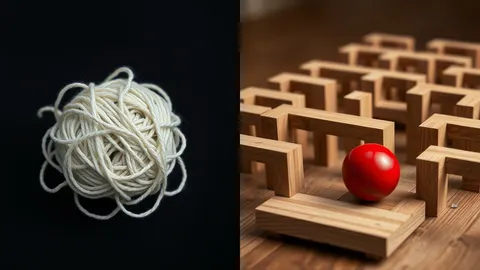
Static analysis finds logic flaws early but misses runtime errors, while dynamic testing catches runtime issues but often misses deep logic bugs.
Account lockout policies reduce brute-force success but create a high risk of denial-of-service against your own user base during coordinated attacks.
Incorrectly configured lockout thresholds allow attackers to enumerate valid usernames before they ever need to guess a password.
Virtual patching intercepts traffic before it reaches the application, allowing defenders to block exploits without touching the underlying code or restarting services.
Silent permission creep often remains invisible until an attacker exfiltrates data, while noisy errors are merely symptoms of deeper policy failures.
Attackers exploit PowerShell’s design as a management tool to execute code in memory, bypassing traditional file-based scanning without triggering standard executable alerts.
DAST reveals runtime flaws like injection attacks that static code scans miss, but it cannot see inside the source code logic itself.
Identity boundaries rarely match network boundaries in hybrid environments, creating blind spots that traditional perimeter tools cannot see or control.
Treating patches as code deployments prevents outages by forcing validation before production exposure and isolating failure points.
Browser extensions operate with elevated permissions that allow them to intercept, modify and inject data into every web page you visit without your explicit knowledge.
Most penetration tests fail because scope ambiguity allows testers to miss critical business logic flaws that automated scans ignore completely.
Bulletproof hosting hides malicious infrastructure behind legal obfuscation and shared resources, making traditional reputation checks insufficient for accurate attribution.
HTTP headers act as strict contracts between server and client, forcing browsers to reject scripts or frames that violate your declared security policies.
Privileged access management shifts security from static credentials to dynamic sessions, reducing the blast radius of compromised admin accounts.
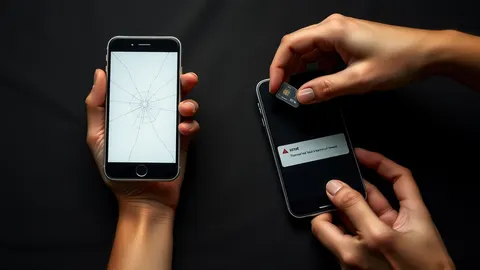
Attackers bypass your phone's security by convincing the carrier to move your number to a new device, rendering two-factor authentication useless.
Stop relying on static signatures. Implement behaviour monitoring and strict access controls to catch code that changes its appearance with every infection.
Establish automated policy enforcement to prevent configuration errors, reduce manual overhead, and maintain security posture without hiring dedicated cloud engineers.