Cyber Attacks
Privileged Access Management: Definition, Purpose and Mechanics
Privileged access management breaks the link between identity and persistent power, ensuring that elevated rights exist only for the duration of a specific task.
Privileged access management breaks the link between identity and persistent power, ensuring that elevated rights exist only for the duration of a specific task.
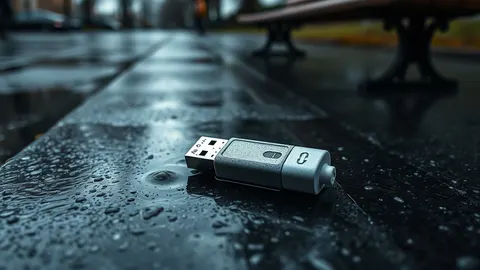
Baiting attacks rarely rely on flashy malware; they succeed by exploiting human curiosity and the lack of visibility into peripheral storage devices.
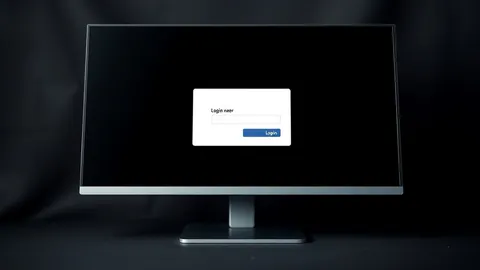
Fake login windows mimic real browser frames to steal credentials from users who trust their own eyes and ignore address bar warnings.
DKIM signatures validate message integrity, not sender identity, meaning a valid signature only proves the content has not changed since the domain owner signed it.
Most phishing simulations fail because they measure click rates rather than the underlying decision-making processes that lead to credential compromise.
Malicious attachments often hide in plain sight by exploiting legacy file formats and abusing legitimate system processes to bypass standard signature-based detection.
Your password manager becomes the single most valuable target for attackers, turning a convenience tool into a high-value honeypot if its own access controls remain weak.
DDoS protection filters traffic by behaviour rather than identity, allowing legitimate users through while silencing the noise of coordinated botnets.
Account lockout policies reduce brute-force success but create a high risk of denial-of-service against your own user base during coordinated attacks.
Incorrectly configured lockout thresholds allow attackers to enumerate valid usernames before they ever need to guess a password.
Privileged access management shifts security from static credentials to dynamic sessions, reducing the blast radius of compromised admin accounts.